Showing posts with label 10. Show all posts
Showing posts with label 10. Show all posts
Sunday, April 30, 2017
¿Cómo instalar Instagram en BlackBerry 10
¿Cómo instalar Instagram en BlackBerry 10

Google Play ID: com.runawaytrips_guides.mallorca
Version: 1.5.12
Size: 32Mb
Mallorca RunAway Travel Guide Screen Preview


Mallorca RunAway Travel Guide Description
The most complete Mallorca travel guide, about travelling, entertainment and services on the island. It will help you discover the island with more than 1000 points of interest and all adhered establishments. No need for 3G and/or data roaming and always up-to-date. Furthermore, with this free Mallorca travel guide, you can create your own route, and take a look at Mallorca with augmented reality. All places at the Mallorca travel guide, have reviews, comments and full descriptions. You can find a universe of possibilities with Mallorca runaway. Now, you can make your own routes from your computer, make any place as favorite and even share them on social networks.Whats new in Mallorca RunAway Travel Guide 1.5.12
New sections. Improved calendar section. Sports and Leisue: before as What to do.Download Mallorca RunAway Travel Guide 1.5.12 APK
Go to link download

Friday, April 28, 2017
Connectify Hotspot Pro 10 Crack Download Full version Latest
Connectify Hotspot Pro 10 Crack Download Full version Latest
Connectify Hotspot Pro 10 Crack Download Full version [Latest]
Go to link download
ESET Internet Security 10 Key Plus Crack Download Free Full Version
ESET Internet Security 10 Key Plus Crack Download Free Full Version
ESET Internet Security 10 Key Plus Crack Download Free Full Version
Go to link download
UC Browser Apk 10 9 Latest Version Download Here
UC Browser Apk 10 9 Latest Version Download Here
UC Browser Apk 10.9 Latest Version Download Here
Go to link download
Good Post Writing Secret! Get Over 10 Thousands Organic Visitors Per Post 2017
Good Post Writing Secret! Get Over 10 Thousands Organic Visitors Per Post 2017
Good and indexed post will have an everlasting performance of driving visitors(Organic traffic) to your blog..Quick tips and tricks that can start working faster.try them Today!
this is the first question you should ask to yourself as it hold a very great impact on your target, that is high quality post content because the writing competition is too big in recent days just as how apple iphone 6 plus is being in writers mind contest. Have you came across the posts which tells that good content must contain 500 to 1000 words? I guess so. But get this, For your post to be very precious to your users and Google bots that ranks and determine the quality of your content with the help of crawlers the content words/content marketing should range above 1500 words.
Hard writing makes easy reading similarly, easy writing makes hard reading. Invest your time on writing. The more time you spend on writing a single post, the more strong and attractive it will be, Trust me or not.What is needed there is just to be Confident and sure of what you are going to flow about. Do you know why am telling this? Its simply because the longer time spent on writing a post will make you to get reflection of very many precious keywords that will boost your post stability.
Keywords; These are words which are likely to be searched by the users on the internet to get relevant content to what they seeks. Now, the good writer usually target to use those strong keywords/AdWords[you can get them from keyword tool or adwords keyword tool] on the first paragraph. Also to those writers who intends to attract high paying Adsense by having the list of keywords for a specific content or niche. They used to put those Keyword just at the start of any paragraph. Keyword highlighting will also help readers to get the whole picture and imagination of what is contained in your post even before they have not read all the stakes that supports the skeleton/ highlighted words
Believe in yourself and what you know, Follow your Passion! You have a definite special skill to share to other, They need your ideas to strengthen them, What are you waiting for?.Most successful writers are those who writes about the stuffs they like. say.. a person who likes technology is likely to write a very good tech post which is full of details and hints
Write, Read, Finish/Conclude, Publish and Learn. Different writers have different writing skills. Example.. by writing the content and read it to know if it real sounds well and it carries what you want it to, If it doesnt satisfy you then thats the right step for you to Edit it before it is Concluded to be published. Learning is the best and super secret of becoming a good writer. Try to read what other writers works and get the tips from their knowledge that you think they gonna boost and improve your posts.
You can not be a great super writer just from the start/beginning. You have to start writing first. No matter how many mistakes you make, the end is gonna be sweet. Trust me or not! But all these will be achieved if you are following the hints, tips and secrets revealed above. You need to be confident of your ideas. Fear is Failure.. avoid it!
Take a look at this full detailed video
Take a look at this full detailed video
Here are some of very useful Secrets and quotes from great writers of all the time
by writersdigest1. Never save your best for last. Start with your best. Expend yourself immediately, then see what happens. The better you do at the beginning, the better you continue to do.
2. The opening paragraph, sentence, line, phrase, word, title—the beginning is the most important part of the work. It sets the tone and lets the readers know you’re a commanding writer.
3. The first duty of a writer is to entertain. Readers lose interest with exposition and abstract philosophy. They want to be entertained. But they feel cheated if, in the course of entertaining, you haven’t taught them something.
4. Show, don’t tell or editorialize. "Not ideas about the thing, but the thing itself."—Wallace Stevens
5. Voice is more important than image. "Poetry is not a thing, but a way of saying it."—A.E. Housman
6. Story is more important than anything. Readers (and publishers) care a lot less about craft than content. The question they ask isn’t, "How accomplished is the writer?" but, "How good is the story?"
7. These rules, pressed far enough, contradict each other. Such is the nature of rules for art.
8. All writing records conflict. Give the opposition quality attention and good lines. The power of the the antagonists should equal that of the protagonists.
9. Shift focus often. Vary sentence structure and type; jump back and forth in time and place; make a good mix of narration, description, exposition and dialogue.
10. Be careful of your diction. A single word, like a drop of iodine in a gallon of water, can change the color of your entire manuscript.
2. The opening paragraph, sentence, line, phrase, word, title—the beginning is the most important part of the work. It sets the tone and lets the readers know you’re a commanding writer.
3. The first duty of a writer is to entertain. Readers lose interest with exposition and abstract philosophy. They want to be entertained. But they feel cheated if, in the course of entertaining, you haven’t taught them something.
4. Show, don’t tell or editorialize. "Not ideas about the thing, but the thing itself."—Wallace Stevens
5. Voice is more important than image. "Poetry is not a thing, but a way of saying it."—A.E. Housman
6. Story is more important than anything. Readers (and publishers) care a lot less about craft than content. The question they ask isn’t, "How accomplished is the writer?" but, "How good is the story?"
7. These rules, pressed far enough, contradict each other. Such is the nature of rules for art.
8. All writing records conflict. Give the opposition quality attention and good lines. The power of the the antagonists should equal that of the protagonists.
9. Shift focus often. Vary sentence structure and type; jump back and forth in time and place; make a good mix of narration, description, exposition and dialogue.
10. Be careful of your diction. A single word, like a drop of iodine in a gallon of water, can change the color of your entire manuscript.
Go to link download
Thursday, April 27, 2017
Monday, April 24, 2017
Terrarium TV – Free and HD TV shows and movies v1 4 10 APK
Terrarium TV – Free and HD TV shows and movies v1 4 10 APK

Terrarium TV
Terrarium is an Android app which allows you to watch, stream and download FREE and HD TV Shows and movies on your Android devices. It provides almost any TV shows and movies. Absolutely free. You can download them on your Android device or watch online.
Features
- FULL HD (1080p) and HD (720p) sources
- Absolutely FREE
- Download and watch offline
- Multi-language subtitles are available
- Fast sources (for Full HD and HD, mostly Google Drive)
- Great amount of TV shows and movies
- Bookmark
- Last watching
- Genre selection
- Chromecast support
MOD Fashion : AD Free / No Update Pop-Up
Screenshot


Requirements
- Android 4.0.1 or upper version
- MXPlayer (Currently the most powerful video player on Android)
Download
Terrarium TV v1.4.10 (Premium) / Mirror
Go to link download
Sunday, April 23, 2017
Facebook messenger ki top 10 hidden tricks hindi me
Facebook messenger ki top 10 hidden tricks hindi me

Hello friends, me is post me aapko facebook messenger ki kuch hidden tricks batane wale hai, jo aapke kafi kaam me aa sakti hai.
facebook ke messenger app me bohot si hidden cheeze hai jo shayad hi aapko pata ho.
yadi me aapko sabhi tricks ke bare me batau to mujhe lagbhag 5000 words ki post likhna padega. isliye han aapko yaha kuch useful tricks hi batayenge.
facebook ke messenger app me bohot si hidden cheeze hai jo shayad hi aapko pata ho.
yadi me aapko sabhi tricks ke bare me batau to mujhe lagbhag 5000 words ki post likhna padega. isliye han aapko yaha kuch useful tricks hi batayenge.
Facebook messenger ki hidden tricks hindi me
1. Add Nickname
Messenger me ham kisi bhi friend ka apni suvidha ke liye nickname add kar sakte hai, kabhi - kabhi ek hi name ke 2-3 friends hote hai ya na bhi ho to bhi aap apni marji se apne manpasand name ko apne friend ka nickname bana sakte hai.
Messenger me nickname kaise add karte hai
Messenger app ko open kare aur jis friend ka nickname add karna hai uske saath conversation launch kare. conversation launch karne karne ke baad upar ki taraf right side me jo Thread detail ka option diya hai usme click kare. (screenshot dekhe)

thread detail option open karne ke baad aapko kuch options show honge unhi me nickname ka bhi option diya hai. nickname ke option me click kare aur aapko jo bhi nickname add karna hai use add karke save kar de.
nickname add karne ke baad aapko us friend ke orignal name ki jagah aapke dwara add kiya gaya nickname hi show hoga.
nickname add karne ke baad aapko us friend ke orignal name ki jagah aapke dwara add kiya gaya nickname hi show hoga.
2. Random Cute
Messenger me aap apne kisi friend ko bina image choose kare simple se messege ko type karke cute si pic send kar sakte hai.
Messenger me random cute pic kaise send kare
Jis friend ko pic send karna hai uske saath conversation launch kare aur messege box me type kare @dailycute aur send kare. messenger aapke liye khud hi ek cute pic send kar dega.
3. Change Conversation Color
Messenge ki conversation ka default color skyblue rehta hai but aap yadi kisi friend ke saath ki conversation ka color change karna chahe to kar sakte hai.
Messenger me conversation color change kaise karte hai
Jis friend ke saath ki conversation ka color change karna hai uske saath conversation launch kare aur thread detail ka option open kare. thread detail option karne baad kuch options diye hue hai unhi me color ka option diya hua hai. color option open kare aur jo bhi color rakhna hai conversation ka use choose karke save kar de.
4. Play Basketball
Messenger ne 13 jun 2016 ke updated version me basketball game add kiya hai. iske liye kisi bhi third party app ko install nahi karna hai. is game ke baare me detail se jaanne ke liye ye post padhe : Facebook messenger me basketball kaise khelte hai.
5. Play Soccer
Messenger ne 13 jun 2016 ke updated version me basketball ke sath soccer game bhi add kiya hai. iske liye bhi koi third party app install nahi karna hai. iske baare me detail se jankari ke liye ye post padhe : Facebook messenger me soccer kaise khelte hai.
6. Play Chess
Ye messenger ka hidden game hai jiske baare me messenger ne apne users ko kisi bhi prakar ki news, notification ya messege nahi diya hai. is game ko khelne ke liye bhi kisi third party app ki jaroorat nahi hai. is game ko khelne ke liye bas kuch simple si commands ka use karna hai. is game ke baare me detail se jankari ke liye ye post padhe : Facebook messenger me chess kaise khelte hai.
7. Voice and Video Call
Messenger me voice aur video call karne ka bhi option hai. jiski madad se aap apne fb friend ko voice aur video calling kar sakte hai but iske liye aap jisko call karenge uske paas bhi messenger hona chahiye.
Messenger me voice and video call kaise karte hai
jis friend ko voice call karna uske sath conversation launch kare aur oopar ki taraf right side me phone ke icon me click kare.
video calling karne ke liye phone ke icon ke side me hi camcorder ka icon hai usme click kare.
video calling karne ke liye phone ke icon ke side me hi camcorder ka icon hai usme click kare.
8. Group Messeges
Messenger me aap apne family members ya kuch friends ka group bana sakte hai aur group messeging kar sakte hai. group ko ek accha sa name bhi de sakte hai.
Facebook messenger me group kaise create karte hai
Messenger me group create karne ke liye kisi bhi friend ke sath conversation launch kare aur thread detail ke option me click kare. thread detail option open hone ke baad create group option me click kare. uske baad group ka name rakhe aur group me members add kare.
9. Share location
Messenger ham apni location apne fb friend ke sath share kar sakte hai.
Facebook messenger me location kaise share karte hai
Sabse pehle apne phone ki location on kare fir jis friend ko location share karna hai uske sath conversation launch kare aur neeche taraf kuch options diye hue hai jisme se ek option me three dots (...) bane hai usme click kare. option open hone ke baad location me click kare uske baad send me click kare.
10. Create Shortcut
Messenger me aap chahe to kisi bhi friends ki conversation ka homepage me shortcut bana sakte hai.
Facebook messenger me conversation ka shortcut kaise banate hai
Messenger open kare aur jis conversation ka shortcut banana hai usme long press kare. long press karne ke baad kuch options show honge unme se create shortcut ke option me click kare.
Friends ummeed hai inme se kuch tricks aapke kaam aayengi. esi aur bhi tricks pane ke liye hamara blog regular visit kare aur hamara fb page like kare.
Go to link download
Friday, April 14, 2017
10 apps a tener en un Samsung Galaxy S4
10 apps a tener en un Samsung Galaxy S4

Google Play ID: com.metromap.krakow.tram
Version: 1.1
Size: 1.7Mb
Krakow Tram Map Screen Preview


Krakow Tram Map Description
Location: Krakow , Poland === Features === - Large Streetcar Map. - No Settings Required. - Pinch to Zoom Capable. - Double Tab to Zoom and Focus. - Once Installed, No Internet Connection Required.Download Krakow Tram Map 1.1 APK
Go to link download
Tuesday, April 11, 2017
10 best new Android apps of February 2017
10 best new Android apps of February 2017
Android apps come out every day that it’s difficult to keep track of them all. It’s difficult to usurp the best of the best but if you’re getting bored with what you’ve got and want to try something new, check out the best new Android apps from the last month!

1. Ever – Capture Your Memories
Everalbum is one of the many photo apps out there trying to pull together all your images from Facebook, Instagram and other popular services to bring them all into one easily-accessed place.
Ever protects your life’s photos so you never have to worry about losing? them. Across devices and photo sources, Ever automatically backs up your photos and videos so you can access them at any time. You can then free up space on your device by removing photos from your camera roll.
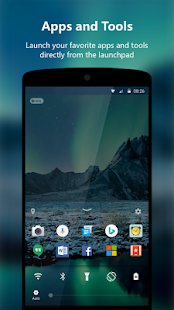
Next Lock Screen is the ultimate lock screen for busy professionals. Next helps protect your phone from unwanted access by others, and you are instantly more productive. It is an excellent productivity locker app and companion for your everyday life.
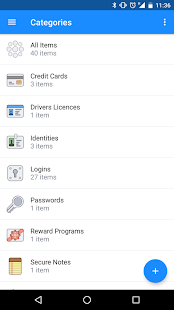
3. 1Password – Password Manager
1Password remembers all your passwords for you, and keeps them safe and secure behind the one password that only you know.
1Password isn’t a new app, but it is a good one and last month’s update on Android brought a long overdue feature – biometric support. That’s right, now you can use your fingerprint reader to log into 1Password and unlock items too.
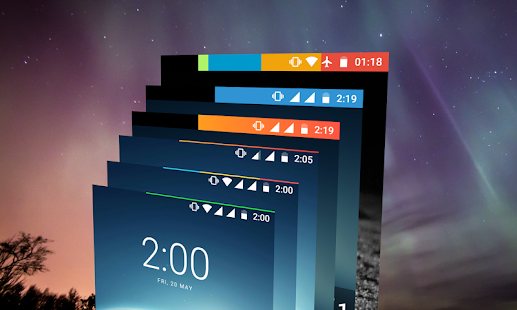
4. Energy Bar
Adds a configurable Energy Bar at the top of your screen indicating current Battery level. And just when you think, such a simple battery bar can display such a crucial information, try plugging in your charger – you’ll be amazed by the details of the animation you’ll see. The pulsating animation and the bar together not only indicates the current Battery level but also how much has the Battery charged since you plugged in your charger.
ADW Launcher 2 has been in beta for a while but had it’s grand re-opening in January. The new ADW has a ton of features, including a modern design, custom widget building, theming, icon pack support, and tons of under the hood changes. The modern design reflects that of other modern browsers such as the Pixel Launcher and Nova Launcher. It also backs up these new features with decent performance and low battery drain.
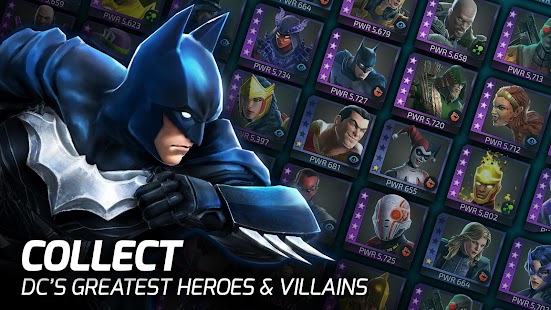
DC Legends features various characters from the DC comics universe, including Batman, Superman, The Joker, and The Flash in RPG-style gameplay. In the game, you collect and form teams of heroes and villains to battle against Nekron and the Manhunters. Each hero/villian has different moves they can perform, so you may have to experiment a bit to progress in the game.
7. SystemPanel 2
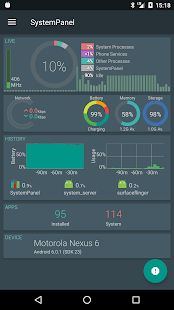
SystemPanel 2 is the latest system monitor app from NextApp. It has been entirely rebuilt from the ground up and looks a lot different from its predecessor. It features Material Design, the ability to monitor most systems from your Android device, and root access for even more stats if you’re rooted. Every feature is available in the free version and the pro version simply removes advertising. The only bad part is that Android Nougat is very strict on what is running on your device. Otherwise, it looks good and it works well.
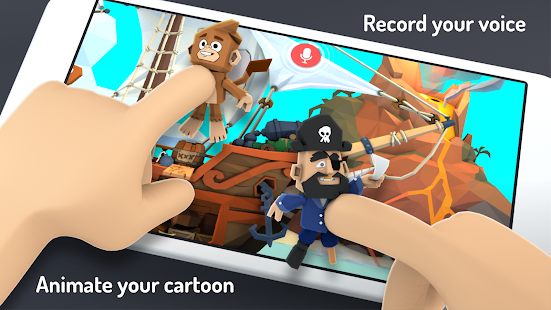
Toontastic 3D is a fun little Google app that lets you create animations. It comes with a variety of characters and objects that you can use to get started. You can also make your own if you’re interested. Along with creating the animations, you can also narrate them, choose from three story arcs to help you along, and you can export the videos and share them when you’re done. It’s not professional level, but it’s still pretty fun to use. It’s also free.
Busuu is another rather well-known app. It features support for about a dozen languages. The app includes the basic stuff like vocabulary and grammar lessons. It also has dialogue and writing lessons to help round out your education. The app boasts that 22.5 hours within its walls are equal to about one semester of college. It focuses on the 150 most important topics and 3000 most commonly used words in each language. Like most, you’ll have to subscribe to get access to everything.
10. Batman: Arkham Underworld
Batman: Arkham Underworld is a strategy adventure game that lets you play with the villains of the Batman universe. You’ll be responsible for creating a hideout, defending it from others in the online PVP, and create guilds with friends. In the game, guilds are referred to as Crime Syndicates. There is also a campaign mode that you can play through. It’s a freemium game and it definitely looks and feels like one. However, it’s a fun little title for Batman fans if you can get passed that. It’s worth a shot at least.
Go to link download
Friday, April 7, 2017
10 Easy Ways to Learn English
10 Easy Ways to Learn English
Hello friends, today we are very much needed in the English language. Every region is being increasingly used in the English language. Learning English is very much on peoples minds when they are afraid of what we will learn?

Listen to English radio stations:
Today, you will easily find many radio channels, you can listen, entertainment, politics, etc. to listen to the news. In addition you can also see the English news channels. See the programs which are of interest to you. Listen to English radio channels even while driving. All these will get used to your ears to hear the English language.
#2. Search YouTube videos and view them on top English:
Top videos are quite handy, because you learn a lot from them.
Comments also read, and write down the words that you have not heard, and they find a means. But note, YouTubes comments are also quite wasteful things.
# Three. Talk to yourself in English and try to sing English songs:
When you are home alone or bath songs in English, and in English by himself speak, about the weather, about the country, etc. This your pronunciation (Pronunciation) certainly will improve.
# Four. Listen to your favorite artists in English interview:
You can do this for hours, and it will not bore you like studying. Hear interviews from your favorite artists will not only entertain you, but you will learn many new things.
# Performer. Sit with people who talk in English:
Just in, office, sit in the park with people who do things in English, and to listen. You can learn a lot by listening.
Not at all shy, look at ways to do their thing, and learn how they are talking to. Czech to understand how much you have to? They speak on different topics.
6. advertising, magazines, etc. Pay attention:
Ads you, to understand what is said about what is in it. Do you understand everything. Try to make the sentence itself and everything around that try to speak in English.
# Seven. Listen to English:
Do you like music, Then listen to English songs, and read his lyrics. Ganos try to understand the meaning, the meaning of words you do not know, find their meaning in the dictionary.
# Delhi. English shows and episodes, see:
It does not matter what they are saying or not they think you did, however, listen, just listen. Try to understand. Read jokes in English. Your heard Chutkulo try to convert the English.
# IX. English people do things on Facebook:
Talking to people on Facebook who are speaking in English, will be your Frandlist many English-speaking news and posts you will see throughout the day in English. Your friend may be your teacher.
# X.. Do not be shy, speak in English as much as possible:
Foreigners who come to visit our country, they spoke English, they will have no trouble with your broken English. You can learn a lot from them. Teachers after class to speak English and to their real concerns. Online shopping and customer care from start to speak in English. If does not matter if you speak slowly. Whether you are a Sikh, it is important.
ReadingkI thanks for Hope You Liked It. Give feedback to these comments, and share these social media
Listen to English radio stations:
Today, you will easily find many radio channels, you can listen, entertainment, politics, etc. to listen to the news. In addition you can also see the English news channels. See the programs which are of interest to you. Listen to English radio channels even while driving. All these will get used to your ears to hear the English language.
#2. Search YouTube videos and view them on top English:
Top videos are quite handy, because you learn a lot from them.
Comments also read, and write down the words that you have not heard, and they find a means. But note, YouTubes comments are also quite wasteful things.
# Three. Talk to yourself in English and try to sing English songs:
When you are home alone or bath songs in English, and in English by himself speak, about the weather, about the country, etc. This your pronunciation (Pronunciation) certainly will improve.
# Four. Listen to your favorite artists in English interview:
You can do this for hours, and it will not bore you like studying. Hear interviews from your favorite artists will not only entertain you, but you will learn many new things.
# Performer. Sit with people who talk in English:
Just in, office, sit in the park with people who do things in English, and to listen. You can learn a lot by listening.
Not at all shy, look at ways to do their thing, and learn how they are talking to. Czech to understand how much you have to? They speak on different topics.
6. advertising, magazines, etc. Pay attention:
Ads you, to understand what is said about what is in it. Do you understand everything. Try to make the sentence itself and everything around that try to speak in English.
# Seven. Listen to English:
Do you like music, Then listen to English songs, and read his lyrics. Ganos try to understand the meaning, the meaning of words you do not know, find their meaning in the dictionary.
# Delhi. English shows and episodes, see:
It does not matter what they are saying or not they think you did, however, listen, just listen. Try to understand. Read jokes in English. Your heard Chutkulo try to convert the English.
# IX. English people do things on Facebook:
Talking to people on Facebook who are speaking in English, will be your Frandlist many English-speaking news and posts you will see throughout the day in English. Your friend may be your teacher.
# X.. Do not be shy, speak in English as much as possible:
Foreigners who come to visit our country, they spoke English, they will have no trouble with your broken English. You can learn a lot from them. Teachers after class to speak English and to their real concerns. Online shopping and customer care from start to speak in English. If does not matter if you speak slowly. Whether you are a Sikh, it is important.
ReadingkI thanks for Hope You Liked It. Give feedback to these comments, and share these social media
Go to link download
Monday, April 3, 2017
10 Useful Android Tips And Tricks You Should Know
10 Useful Android Tips And Tricks You Should Know
Android is a great little operating system. It’s absolutely packed with great features , awesome hacks , and time-saving tricks.
But how much do you really know about your phone or tablet ?
Sure, you can make phone calls and send texts, but we bet there is something in this article that you weren’t aware of.
Read on to find out!

1. Disable App Notifications
Bugged by annoying app notifications that just keep coming? If you don’t know already, these app notifications also drain your phone’s battery. If you want to turn them off, and you are on Jelly Bean 4.1 and above, here’s how:
A. On any of your unwanted notifications in your notification bar, long press on the notification for a message box to appear.
B. Tap on App Info > Untick Show Notifications >
OK .
2. Disable Mobile Data
Whenever you don’t need to stay connected, disabling the Mobile Data can help keep your smartphone battery from draining too quickly. Turning off mobile data is as easy as:
A. Going to Settings > Data Usage.
B. Disable Mobile data by toggling the setting from ON to OFF .
3. Ensure your device gets back to you if you lose it.
There’s no surefire way to guarantee you’ll ever see your phone or tablet again if you leave it out in public by accident. That being said, you can improve the chances of it being returned to you by editing your security settings. Go to settings, then security, then owner info. There you’ll see a little box where you can type in contact information that will show up on your lockscreen. This will make it easier for a good Samaritan to return a lost device to its rightful owner.
4. Say “Ok, Google” to start a search from any screen.
It’s the 21 century and we’re all busy 24/7. Cut down on the time it takes to manually search for things by doing it with your voice. To activate vocal control over Google searches, go to your apps page and find the Google app. Tap it (it should take you to Google Now), and scroll down until you see the settings icon on the bottom right. Hit that and select “Voice.” Then, tap on “Ok Google Detection” and activate the “From any screen” setting. Now you’ll be able to start a Google search from any screen on your phone simply by speaking the phrase, “Ok, Google.”
5. You aren’t tied to the Google Play store.
OK, well, you sort of are, but you can download other app stores like Amazon’s if you want to. Indeed, I highly suggest you do so because they are always offering insane deals to try and rip you away from Google’s warm embrace. One of these is their “App of the Day,” in which Amazon offers up a free app to entice you to spend more time in their store. If you’re lucky, you’ll be able to save lots of money using these promotions, as at times they’ll put up apps for free that cost several dollars on Google Play.
6. How to Turn Off Auto-Correction
Hate the fact that your phone is going English teacher mode on you? Turn off auto-correction for peace of mind when texting.
1. Go to Settings > Language & input.
2. Tap on the settings icon next to the keyboard that you are using, e.g. Google Keyboard.
3. Look for Auto-correction and tap on it.
4. Select Off to turn auto-correction off.
7. Disable Animations
Here’s a tip on how to make your Android device run a bit smoother: disable its animations. You will need to have access to Developer Options which can be found under Settings or About device.
Note: For some phones, you may need to go to Build number and tap on it repeatedly until you see “You are now a developer!”. Developer options are now enabled.
Under enabled Developer options , look for
Window animation scale, Transition animation scale, and Animator duration scale. Then, turn them off (disable) them one at a time.
8. Make your phone harder to break into than Fort Knox.
Reader warning: don’t do this one unless you’re really afraid of your phone’s information being stolen. To permanently encrypt your Android device, go to settings, security, encryption, and tap “Encrypt phone.” You’ll then be required to create a pin, which you’ll enter every time you turn your phone on (in order to decrypt it). This is like the unlock code on an iPhone, except way more drastic. Usually it will take about an hour for your device to encrypt itself, and it can only be undone through a factory reset. Only do this if you have sensitive information, or want your phone to be as secure as humanly possible. Be aware that encrypting your information will slow down how fast you can access it.
9. AVE BATTERY BY TURNING OFF POWER-DRAINING APPS
If your battery is dying too quickly, it might be because of background apps that you forget are running. Beefing up your battery life can be easier than you think.
Navigate to Settings>>Apps>>then swipe to the "running" tab. Youll see the apps that are using the most processing and battery power. If you dont use a high-power app very often, simply tap the app and then tap the "quit" button. Getting rid of energy-sucking apps should give you a small boost to your battery life.
10. SET QUICK RESPONSES FOR MISSED CALLS
Have you ever gotten a call from someone just before you head into a movie? Itd be rude to get your phone out to respond, but you dont want them to feel like youre giving them the cold shoulder.
Writing a quick response can solve that very problem. Navigate to Settings>>Call Settings>>Quick Response.
But how much do you really know about your phone or tablet ?
Sure, you can make phone calls and send texts, but we bet there is something in this article that you weren’t aware of.
Read on to find out!
1. Disable App Notifications
Bugged by annoying app notifications that just keep coming? If you don’t know already, these app notifications also drain your phone’s battery. If you want to turn them off, and you are on Jelly Bean 4.1 and above, here’s how:
A. On any of your unwanted notifications in your notification bar, long press on the notification for a message box to appear.
B. Tap on App Info > Untick Show Notifications >
OK .
2. Disable Mobile Data
Whenever you don’t need to stay connected, disabling the Mobile Data can help keep your smartphone battery from draining too quickly. Turning off mobile data is as easy as:
A. Going to Settings > Data Usage.
B. Disable Mobile data by toggling the setting from ON to OFF .
3. Ensure your device gets back to you if you lose it.
There’s no surefire way to guarantee you’ll ever see your phone or tablet again if you leave it out in public by accident. That being said, you can improve the chances of it being returned to you by editing your security settings. Go to settings, then security, then owner info. There you’ll see a little box where you can type in contact information that will show up on your lockscreen. This will make it easier for a good Samaritan to return a lost device to its rightful owner.
4. Say “Ok, Google” to start a search from any screen.
It’s the 21 century and we’re all busy 24/7. Cut down on the time it takes to manually search for things by doing it with your voice. To activate vocal control over Google searches, go to your apps page and find the Google app. Tap it (it should take you to Google Now), and scroll down until you see the settings icon on the bottom right. Hit that and select “Voice.” Then, tap on “Ok Google Detection” and activate the “From any screen” setting. Now you’ll be able to start a Google search from any screen on your phone simply by speaking the phrase, “Ok, Google.”
5. You aren’t tied to the Google Play store.
OK, well, you sort of are, but you can download other app stores like Amazon’s if you want to. Indeed, I highly suggest you do so because they are always offering insane deals to try and rip you away from Google’s warm embrace. One of these is their “App of the Day,” in which Amazon offers up a free app to entice you to spend more time in their store. If you’re lucky, you’ll be able to save lots of money using these promotions, as at times they’ll put up apps for free that cost several dollars on Google Play.
6. How to Turn Off Auto-Correction
Hate the fact that your phone is going English teacher mode on you? Turn off auto-correction for peace of mind when texting.
1. Go to Settings > Language & input.
2. Tap on the settings icon next to the keyboard that you are using, e.g. Google Keyboard.
3. Look for Auto-correction and tap on it.
4. Select Off to turn auto-correction off.
7. Disable Animations
Here’s a tip on how to make your Android device run a bit smoother: disable its animations. You will need to have access to Developer Options which can be found under Settings or About device.
Note: For some phones, you may need to go to Build number and tap on it repeatedly until you see “You are now a developer!”. Developer options are now enabled.
Under enabled Developer options , look for
Window animation scale, Transition animation scale, and Animator duration scale. Then, turn them off (disable) them one at a time.
8. Make your phone harder to break into than Fort Knox.
Reader warning: don’t do this one unless you’re really afraid of your phone’s information being stolen. To permanently encrypt your Android device, go to settings, security, encryption, and tap “Encrypt phone.” You’ll then be required to create a pin, which you’ll enter every time you turn your phone on (in order to decrypt it). This is like the unlock code on an iPhone, except way more drastic. Usually it will take about an hour for your device to encrypt itself, and it can only be undone through a factory reset. Only do this if you have sensitive information, or want your phone to be as secure as humanly possible. Be aware that encrypting your information will slow down how fast you can access it.
9. AVE BATTERY BY TURNING OFF POWER-DRAINING APPS
If your battery is dying too quickly, it might be because of background apps that you forget are running. Beefing up your battery life can be easier than you think.
Navigate to Settings>>Apps>>then swipe to the "running" tab. Youll see the apps that are using the most processing and battery power. If you dont use a high-power app very often, simply tap the app and then tap the "quit" button. Getting rid of energy-sucking apps should give you a small boost to your battery life.
10. SET QUICK RESPONSES FOR MISSED CALLS
Have you ever gotten a call from someone just before you head into a movie? Itd be rude to get your phone out to respond, but you dont want them to feel like youre giving them the cold shoulder.
Writing a quick response can solve that very problem. Navigate to Settings>>Call Settings>>Quick Response.
Go to link download
Wireshark v1 10 8 The world’s foremost network protocol analyzer
Wireshark v1 10 8 The world’s foremost network protocol analyzer

Wireshark is the world’s foremost network protocol analyzer. It lets you capture and interactively browse the traffic running on a computer network. It is the de facto (and often de jure) standard across many industries and educational institutions.
Wireshark development thrives thanks to the contributions of networking experts across the globe. It is the continuation of a project that started in 1998.
Features
Wireshark has a rich feature set which includes the following:- Deep inspection of hundreds of protocols, with more being added all the time
- Live capture and offline analysis
- Standard three-pane packet browser
- Multi-platform: Runs on Windows, Linux, OS X, Solaris, FreeBSD, NetBSD, and many others
- Captured network data can be browsed via a GUI, or via the TTY-mode TShark utility
- The most powerful display filters in the industry
- Rich VoIP analysis
- Read/write many different capture file formats: tcpdump (libpcap), Pcap NG, Catapult DCT2000, Cisco Secure IDS iplog, Microsoft Network Monitor, Network General Sniffer® (compressed and uncompressed), Sniffer® Pro, and NetXray®, Network Instruments Observer, NetScreen snoop, Novell LANalyzer, RADCOM WAN/LAN Analyzer, Shomiti/Finisar Surveyor, Tektronix K12xx, Visual Networks Visual UpTime, WildPackets EtherPeek/TokenPeek/AiroPeek, and many others
- Capture files compressed with gzip can be decompressed on the fly
- Live data can be read from Ethernet, IEEE 802.11, PPP/HDLC, ATM, Bluetooth, USB, Token Ring, Frame Relay, FDDI, and others (depending on your platform)
- Decryption support for many protocols, including IPsec, ISAKMP, Kerberos, SNMPv3, SSL/TLS, WEP, and WPA/WPA2
- Coloring rules can be applied to the packet list for quick, intuitive analysis
- Output can be exported to XML, PostScript®, CSV, or plain text
Changelog:
The following vulnerabilities have been fixed.
The following bugs have been fixed:
- wnpa-sec-2014-07The frame metadissector could crash. (Bug 9999, Bug 10030)Versions affected: 1.10.0 to 1.10.7CVE-2014-4020
- VoIP flow graph crash upon opening. (Bug 9179)
- Tshark with "-F pcap" still generates a pcapng file. (Bug 9991)
- IPv6 Next Header 0x3d recognized as SHIM6. (Bug 9995)
- Failed to export pdml on large pcap. (Bug 10081)
- TCAP: set a fence on info column after calling sub dissector (Bug 10091)
- Dissector bug in JSON protocol. (Bug 10115)
- GSM RLC MAC: do not skip too many lines of the CSN_DESCR when the field is missing (Bug 10120)
- Wireshark PEEKREMOTE incorrectly decoding QoS data packets from Cisco Sniffer APs. (Bug 10139)
- IEEE 802.11: fix dissection of HT Capabilities (Bug 10166)
Download Wireshark
Go to link download
Sunday, April 2, 2017
BlackArch Linux v2014 10 07 Lightweight expansion to Arch Linux for pentesters and security researchers
BlackArch Linux v2014 10 07 Lightweight expansion to Arch Linux for pentesters and security researchers

BlackArch Linux ISOs including more than 1000 tools and lots of improvements. Also, armv6h and armv7h repositories are filled with more than 1050 tools.
A short ChangeLog:
- - tool fix: beef
- - fixed pam issues
- - added services and login.defs file
- - removed kde/openbox and i3-debug menu items from lxdm
- - fixed blackarch keyring issue
- - disabled dhcpcd service
- - upgraded menu entries for awesome, openbox and fluxbox
- - upgraded tools
- - added a bunch of new tools (contains now more than 1050 tools)
- - upgraded archiso profile
- - and more ...
Tool count: 1067
| Name | Version | Description | Homepage |
|---|---|---|---|
| 0trace | 1.5 | A hop enumeration tool | http://jon.oberheide.org/0trace/ |
| 3proxy | 0.7.1.1 | Tiny free proxy server. | http://3proxy.ru/ |
| 3proxy-win32 | 0.7.1.1 | Tiny free proxy server. | http://3proxy.ru/ |
| 42zip | 42 | Recursive Zip archive bomb. | http://blog.fefe.de/?ts=b6cea88d |
| acccheck | 0.2.1 | A password dictionary attack tool that targets windows authentication via the SMB protocol. | http://labs.portcullis.co.uk/tools/acccheck/ |
| ace | 1.10 | Automated Corporate Enumerator. A simple yet powerful VoIP Corporate Directory enumeration tool that mimics the behavior of an IP Phone in order to download the name and extension entries that a given phone can display on its screen interface | http://ucsniff.sourceforge.net/ace.html |
| admid-pack | 0.1 | ADM DNS spoofing tools - Uses a variety of active and passive methods to spoof DNS packets. Very powerful. | http://packetstormsecurity.com/files/10080/ADMid-pkg.tgz.html |
| adminpagefinder | 0.1 | This python script looks for a large amount of possible administrative interfaces on a given site. | http://packetstormsecurity.com/files/112855/Admin-Page-Finder-Script.html |
| admsnmp | 0.1 | ADM SNMP audit scanner. | |
| aesfix | 1.0.1 | A tool to find AES key in RAM | http://citp.princeton.edu/memory/code/ |
| aeskeyfind | 1.0 | A tool to find AES key in RAM | http://citp.princeton.edu/memory/code/ |
| aespipe | 2.4c | Reads data from stdin and outputs encrypted or decrypted results to stdout. | http://loop-aes.sourceforge.net/aespipe/ |
| afflib | 3.7.1 | An extensible open format for the storage of disk images and related forensic information | http://www.afflib.org |
| afpfs-ng | 0.8.1 | A client for the Apple Filing Protocol (AFP) | http://alexthepuffin.googlepages.com/ |
| against | 0.2 | A very fast ssh attacking script which includes a multithreaded port scanning module (tcp connect) for discovering possible targets and a multithreaded brute-forcing module which attacks parallel all discovered hosts or given ip addresses from a list. | http://nullsecurity.net/tools/cracker.html |
| aiengine | 315.7d1c555 | A packet inspection engine with capabilities of learning without any human intervention. | https://bitbucket.org/camp0/aiengine/ |
| aimage | 3.2.5 | A program to create aff-images. | http://www.afflib.org |
| air | 2.0.0 | A GUI front-end to dd/dc3dd designed for easily creating forensic images. | http://air-imager.sourceforge.net/ |
| airflood | 0.1 | A modification of aireplay that allows for a DOS in in the AP. This program fills the table of clients of the AP with random MACs doing impossible new connections. | http://packetstormsecurity.com/files/51127/airflood.1.tar.gz.html |
| airgraph-ng | 2371 | Graphing tool for the aircrack suite | http://www.aircrack-ng.org |
| airoscript | 45.0a122ee | A script to simplify the use of aircrack-ng tools. | http://midnightresearch.com/projects/wicrawl/ |
| airpwn | 1.4 | A tool for generic packet injection on an 802.11 network. | http://airpwn.sourceforge.net |
| allthevhosts | 1.0 | A vhost discovery tool that scrapes various web applications | http://labs.portcullis.co.uk/tools/finding-all-the-vhosts/ |
| androguard | 1.9 | Reverse engineering, Malware and goodware analysis of Android applications and more. | https://code.google.com/p/androguard/ |
| android-apktool | 1.5.2 | A tool for reengineering Android apk files. | http://forum.xda-developers.com/showthread.php?t=1755243 |
| android-ndk | r9c | Android C/C++ developer kit. | http://developer.android.com/sdk/ndk/index.html |
| android-sdk-platform-tools | r19 | Platform-Tools for Google Android SDK (adb and fastboot) | http://developer.android.com/sdk/index.html |
| android-sdk | r22.3 | Google Android SDK | http://developer.android.com/sdk/index.html |
| android-udev-rules | 8181.da07974 | Android udev rules. | https://github.com/bbqlinux/android-udev-rules |
| androidsniffer | 0.1 | A perl script that lets you search for 3rd party passwords, dump the call log, dump contacts, dump wireless configuration, and more. | http://packetstormsecurity.com/files/97464/Andr01d-Magic-Dumper.1.html |
| anontwi | 1.0 | A free software python client designed to navigate anonymously on social networks. It supports Identi.ca and Twitter.com. | http://anontwi.sourceforge.net/ |
| aphopper | 0.3 | AP Hopper is a program that automatically hops between access points of different wireless networks. | http://aphopper.sourceforge.net/ |
| apnbf | 0.1 | A small python script designed for enumerating valid APNs (Access Point Name) on a GTP-C speaking device. | http://www.c0decafe.de/ |
| arachni | 1.0.2 | A feature-full, modular, high-performance Ruby framework aimed towards helping penetration testers and administrators evaluate the security of web applications. | https://www.arachni-scanner.com |
| arduino | 1.0.5 | Arduino SDK (includes patched avrdude and librxtx) | http://arduino.cc/en/Main/Software |
| argus | 3.0.6.1 | Network monitoring tool with flow control. | http://qosient.com/argus/ |
| argus-clients | 3.0.6.2 | Network monitoring client for Argus. | http://qosient.com/argus/ |
| armitage | 140715 | A graphical cyber attack management tool for Metasploit. | http://www.fastandeasyhacking.com/ |
| arp-scan | 1.9 | A tool that uses ARP to discover and fingerprint IP hosts on the local network | http://www.nta-monitor.com/tools/arp-scan/ |
| arpalert | 2.0.12 | Monitor ARP changes in ethernet networks | http://www.arpalert.org/ |
| arpantispoofer | 1.0.1.32 | A utility to detect and resist BIDIRECTIONAL ARP spoofing. It can anti-spoof for not only the local host, but also other hosts in the same subnet. It is also a handy helper for gateways which dont work well with ARP. | http://arpantispoofer.sourceforge.net/ |
| arpoison | 0.6 | The UNIX arp cache update utility | http://www.arpoison.net |
| arpon | 2.7 | A portable handler daemon that make ARP protocol secure in order to avoid the Man In The Middle (MITM) attack through ARP Spoofing, ARP Cache Poisoning or ARP Poison Routing (APR) attacks. | http://arpon.sourceforge.net/ |
| arpwner | 26.f300fdf | GUI-based python tool for arp posioning and dns poisoning attacks. | https://github.com/ntrippar/ARPwner |
| artillery | 1.0.2 | A combination of a honeypot, file-system monitoring, system hardening, and overall health of a server to create a comprehensive way to secure a system | https://www.trustedsec.com/downloads/artillery/ |
| asleap | 2.2 | Actively recover LEAP/PPTP passwords. | http://www.willhackforsushi.com/Asleap.html |
| asp-audit | 2BETA | An ASP fingerprinting tool and vulnerability scanner. | http://seclists.org/basics/2006/Sep/128 |
| athena-ssl-scanner | 0.5.2 | a SSL cipher scanner that checks all cipher codes. It can identify about 150 different ciphers. | http://packetstormsecurity.com/files/93062/Athena-SSL-Cipher-Scanner.html |
| atstaketools | 0.1 | This is an archive of various @Stake tools that help perform vulnerability scanning and analysis, information gathering, password auditing, and forensics. | http://packetstormsecurity.com/files/50718/AtStakeTools.zip.html |
| auto-xor-decryptor | 3.6a1f8f7 | Automatic XOR decryptor tool. | http://www.blog.mrg-effitas.com/publishing-of-mrg-effitas-automatic-xor-decryptor-tool/ |
| autopsy | 2.24 | A GUI for The Sleuth Kit. | http://www.sleuthkit.org/autopsy |
| azazel | 10.401e3aa | A userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. | https://github.com/chokepoint/azazel |
| b2sum | 20140114 | BLAKE2 file hash sum check. Computes the BLAKE2 (BLAKE2b or -s, -bp, -sp) cryptographic hash of a given file. | https://blake2.net/ |
| backcookie | 34.66b0a27 | Small backdoor using cookie. | https://github.com/mrjopino/backcookie |
| backdoor-factory | 91.20fe713 | Patch win32/64 binaries with shellcode. | https://github.com/secretsquirrel/the-backdoor-factory |
| backfuzz | 36.8e54ed6 | A network protocol fuzzing toolkit. | https://github.com/localh0t/backfuzz |
| balbuzard | 65.546c5dcf629c | A package of malware analysis tools in python to extract patterns of interest from suspicious files (IP addresses, domain names, known file headers, interesting strings, etc). | https://bitbucket.org/decalage/balbuzard/ |
| bamf-framework | 35.30d2b4b | A modular framework designed to be a platform to launch attacks against botnets. | https://github.com/bwall/BAMF |
| basedomainname | 0.1 | Tool that can extract TLD (Top Level Domain), domain extensions (Second Level Domain + TLD), domain name, and hostname from fully qualified domain names. | http://www.morningstarsecurity.com/research |
| batman-adv | 2013.4.0 | batman kernel module, (included upstream since .38) | http://www.open-mesh.net/ |
| bbqsql | 1.2 | SQL injection exploitation tool. | https://github.com/neohapsis/bbqsql |
| bdfproxy | 37.7b6221b | Patch Binaries via MITM: BackdoorFactory + mitmProxy | https://github.com/secretsquirrel/BDFProxy |
| bed | 0.5 | Collection of scripts to test for buffer overflows, format string vulnerabilities. | http://www.aldeid.com/wiki/Bed |
| beef | 0.4.5.0.118.g9e43f0b | The Browser Exploitation Framework that focuses on the web browser | http://beefproject.com/ |
| beholder | 0.8.9 | A wireless intrusion detection tool that looks for anomalies in a wifi environment. | http://www.beholderwireless.org/ |
| beleth | 36.0963699 | A Multi-threaded Dictionary based SSH cracker. | https://github.com/chokepoint/Beleth |
| bfbtester | 2.0.1 | Performs checks of single and multiple argument command line overflows and environment variable overflows | http://sourceforge.net/projects/bfbtester/ |
| bgp-md5crack | 0.1 | RFC2385 password cracker | http://www.c0decafe.de/ |
| bing-ip2hosts | 0.4 | Enumerates all hostnames which Bing has indexed for a specific IP address. | http://www.morningstarsecurity.com/research/bing-ip2hosts |
| bing-lfi-rfi | 0.1 | This is a python script for searching Bing for sites that may have local and remote file inclusion vulnerabilities. | http://packetstormsecurity.com/files/121590/Bing-LFI-RFI-Scanner.html |
| binwalk | 2.0.1 | A tool for searching a given binary image for embedded files. | http://binwalk.org |
| binwally | 3.ca092a7 | Binary and Directory tree comparison tool using the Fuzzy Hashing concept (ssdeep). | https://github.com/bmaia/binwally |
| bios_memimage | 1.2 | A tool to dump RAM contents to disk (aka cold boot attack). | http://citp.princeton.edu/memory/code/ |
| birp | 60.1d7c49f | A tool that will assist in the security assessment of mainframe applications served over TN3270. | https://github.com/sensepost/birp |
| bittwist | 2.0 | A simple yet powerful libpcap-based Ethernet packet generator. It is designed to complement tcpdump, which by itself has done a great job at capturing network traffic. | http://bittwist.sourceforge.net/ |
| bkhive | 1.1.1 | Program for dumping the syskey bootkey from a Windows NT/2K/XP system hive. | http://sourceforge.net/projects/ophcrack |
| blackarch-menus | 0.2 | BlackArch specific XDG-compliant menu | http://www.blackarch.org/ |
| blackhash | 0.2 | Creates a filter from system hashes | http://16s.us/blackhash/ |
| bletchley | 0.0.1 | A collection of practical application cryptanalysis tools. | https://code.google.com/p/bletchley/ |
| blindelephant | 7 | A web application fingerprinter. Attempts to discover the version of a (known) web application by comparing static files at known locations | http://blindelephant.sourceforge.net/ |
| blindsql | 1.0 | Set of bash scripts for blind SQL injection attacks | http://www.enye-sec.org/programas.html |
| bluebox-ng | 65.33a19a8 | A GPL VoIP/UC vulnerability scanner. | https://github.com/jesusprubio/bluebox-ng |
| bluebugger | 0.1 | An implementation of the bluebug technique which was discovered by Martin Herfurt. | http://packetstormsecurity.com/files/54024/bluebugger.1.tar.gz.html |
| bluelog | 1.1.1 | A Bluetooth scanner and sniffer written to do a single task, log devices that are in discoverable mode. | http://www.digifail.com/software/bluelog.shtml |
| bluepot | 0.1 | A Bluetooth Honeypot written in Java, it runs on Linux | https://code.google.com/p/bluepot/ |
| blueprint | 0.1_3 | A perl tool to identify Bluetooth devices. | http://trifinite.org/trifinite_stuff_blueprinting.html |
| blueranger | 1.0 | A simple Bash script which uses Link Quality to locate Bluetooth device radios. | http://www.hackfromacave.com/projects/blueranger.html |
| bluesnarfer | 0.1 | A bluetooth attacking tool | http://www.alighieri.org/project.html |
| bmap-tools | 3.2 | Tool for copying largely sparse files using information from a block map file. | http://git.infradead.org/users/dedekind/bmap-tools.git |
| bob-the-butcher | 0.7.1 | A distributed password cracker package. | http://btb.banquise.net/ |
| bokken-hg | 370.b180f39d107f | GUI for radare2 and pyew. | http://inguma.eu/projects/bokken/ |
| bowcaster | 0.1 | This framework, implemented in Python, is intended to aid those developing exploits by providing useful set of tools and modules, such as payloads, encoders, connect-back servers, etc. Currently the framework is focused on the MIPS CPU architecture, but the design is intended to be modular enough to support arbitrary architectures. | https://github.com/zcutlip/bowcaster |
| braa | 0.82 | A mass snmp scanner | http://s-tech.elsat.net.pl/braa/ |
| braces | 0.4 | A Bluetooth Tracking Utility. | http://braces.shmoo.com/ |
| browser-fuzzer | 3 | Browser Fuzzer 3 | http://www.krakowlabs.com/dev.html |
| brutessh | 0.5 | A simple sshd password bruteforcer using a wordlist, its very fast for internal networks. Its multithreads. | http://www.edge-security.com/edge-soft.php |
| brutus | 2 | One of the fastest, most flexible remote password crackers you can get your hands on. | http://www.hoobie.net/brutus/ |
| bsdiff | 4.3 | bsdiff and bspatch are tools for building and applying patches to binary files. | http://www.daemonology.net/bsdiff/ |
| bsqlbf | 2.6 | Blind SQL Injection Brute Forcer. | http://code.google.com/p/bsqlbf-v2/ |
| bss | 0.8 | Bluetooth stack smasher / fuzzer | http://www.secuobs.com/news/15022006-bss_0_8.shtml |
| bt_audit | 0.1.1 | Bluetooth audit | http://www.betaversion.net/btdsd/download/ |
| btcrack | 1.1 | The worlds first Bluetooth Pass phrase (PIN) bruteforce tool. Bruteforces the Passkey and the Link key from captured Pairing exchanges. | http://www.nruns.com/_en/security_tools_btcrack.php |
| btscanner | 2.1 | Bluetooth device scanner. | http://www.pentest.co.uk |
| bulk-extractor | 1.3.1 | Bulk Email and URL extraction tool | https://github.com/simsong/bulk_extractor |
| bully | 23.1fef73a | A wifi-protected-setup (WPS) brute force attack tool. | http://code.google.com/p/bully/ |
| bunny | 0.93 | A closed loop, high-performance, general purpose protocol-blind fuzzer for C programs. | http://code.google.com/p/bunny-the-fuzzer/ |
| burpsuite | 1.6 | An integrated platform for attacking web applications (free edition). | http://portswigger.net/burp/ |
| buttinsky | 138.1a2a1b2 | Provide an open source framework for automated botnet monitoring. | https://github.com/buttinsky/buttinsky |
| bvi | 1.4.0beta | A display-oriented editor for binary files operate like "vi" editor. | http://bvi.sourceforge.net/ |
| cadaver | 0.23.3 | Command-line WebDAV client for Unix | http://www.webdav.org/cadaver |
| canari | 1.1 | A transform framework for maltego | http://www.canariproject.com/ |
| cansina | 93.abc6577 | A python-based Web Content Discovery Tool. | https://github.com/deibit/cansina |
| capstone | 2.1.2 | A lightweight multi-platform, multi-architecture disassembly framework. | http://www.capstone-engine.org/index.html |
| carwhisperer | 0.2 | Intends to sensibilise manufacturers of carkits and other Bluetooth appliances without display and keyboard for the possible security threat evolving from the use of standard passkeys. | http://trifinite.org/trifinite_stuff_carwhisperer.html |
| casefile | 1.0.1 | The little brother to Maltego without transforms, but combines graph and link analysis to examine links between manually added data to mind map your information | http://www.paterva.com/web6/products/casefile.php |
| cdpsnarf | 0.1.6 | Cisco discovery protocol sniffer. | https://github.com/Zapotek/cdpsnarf |
| cecster | 5.15544cb | A tool to perform security testing against the HDMI CEC (Consumer Electronics Control) and HEC (HDMI Ethernet Channel) protocols | https://github.com/nccgroup/CECster |
| centry | 72.6de2868 | Cold boot & DMA protection | https://github.com/0xPoly/Centry |
| cewl | 4.3 | A custom word list generator | http://www.digininja.org/projects/cewl.php |
| cflow | 1.4 | A C program flow analyzer. | http://www.gnu.org/software/cflow/ |
| chaosmap | 1.3 | An information gathering tool and dns / whois / web server scanner | http://freecode.com/projects/chaosmap |
| chaosreader | 0.94 | A freeware tool to trace tcp, udp etc. sessions and fetch application data from snoop or tcpdump logs. | http://chaosreader.sourceforge.net/ |
| chapcrack | 17.ae2827f | A tool for parsing and decrypting MS-CHAPv2 network handshakes. | https://github.com/moxie0/chapcrack |
| check-weak-dh-ssh | 0.1 | Debian OpenSSL weak client Diffie-Hellman Exchange checker. | http://packetstormsecurity.com/files/66683/check_weak_dh_ssh.pl.bz2.html |
| checkiban | 0.2 | Checks the validity of an International Bank Account Number (IBAN). | http://kernel.embedromix.ro/us/ |
| checkpwd | 1.23 | Oracle Password Checker (Cracker) | http://www.red-database-security.com/software/checkpwd.html |
| checksec | 1.5 | The checksec.sh script is designed to test what standard Linux OS and PaX security features are being used. | http://www.trapkit.de/tools/checksec.html |
| chiron | 0.1 | An all-in-one IPv6 Penetration Testing Framework. | http://www.secfu.net/tools-scripts/ |
| chkrootkit | 0.50 | Checks for rootkits on a system | http://www.chkrootkit.org/ |
| chntpw | 140201 | Offline NT Password Editor - reset passwords in a Windows NT SAM user database file | http://pogostick.net/~pnh/ntpasswd/ |
| chownat | 0.08b | Allows two peers behind two separate NATs with no port forwarding and no DMZ setup on their routers to directly communicate with each other | http://samy.pl/chownat/ |
| chrome-decode | 0.1 | Chrome web browser decoder tool that demonstrates recovering passwords. | http://packetstormsecurity.com/files/119153/Chrome-Web-Browser-Decoder.html |
| chromefreak | 22.336e323 | A Cross-Platform Forensic Framework for Google Chrome | http://osandamalith.github.io/ChromeFreak/ |
| cidr2range | 0.9 | Script for listing the IP addresses contained in a CIDR netblock | http://www.cpan.org/authors/id/R/RA/RAYNERLUC |
| cintruder | 0.2.0 | An automatic pentesting tool to bypass captchas. | http://cintruder.sourceforge.net/ |
| ciphertest | 4.5780d36 | A better SSL cipher checker using gnutls. | https://github.com/OpenSecurityResearch/ciphertest |
| cirt-fuzzer | 1.0 | A simple TCP/UDP protocol fuzzer. | http://www.cirt.dk/ |
| cisco-auditing-tool | 1 | Perl script which scans cisco routers for common vulnerabilities. Checks for default passwords, easily guessable community names, and the IOS history bug. Includes support for plugins and scanning multiple hosts. | http://www.scrypt.net |
| cisco-global-exploiter | 1.3 | A perl script that targets multiple vulnerabilities in the Cisco Internetwork Operating System (IOS) and Catalyst products. | http://www.blackangels.it |
| cisco-ocs | 0.2 | Cisco Router Default Password Scanner. | http://www.question-defense.com/2013/01/11/ocs-version-2-release-ocs-cisco-router-default-password-scanner |
| cisco-router-config | 1.1 | copy-router-config and merge-router-config to copy and merge Cisco Routers Configuration | |
| cisco-scanner | 0.2 | Multithreaded Cisco HTTP vulnerability scanner. Tested on Linux, OpenBSD and Solaris. | http://wayreth.eu.org/old_page/ |
| cisco-torch | 0.4b | Cisco Torch mass scanning, fingerprinting, and exploitation tool. | http://www.arhont.com |
| cisco5crack | 2.c4b228c | Crypt and decrypt the cisco enable 5 passwords. | https://github.com/madrisan/cisco7crack |
| cisco7crack | 2.f1c21dd | Crypt and decrypt the cisco enable 7 passwords. | https://github.com/madrisan/cisco7crack |
| ciscos | 1.3 | Scans class A, B, and C networks for cisco routers which have telnet open and have not changed the default password from cisco. | |
| climber | 23.f614304 | Check UNIX/Linux systems for privilege escalation. | https://github.com/raffaele-forte/climber |
| clusterd | 129.0f04a49 | Automates the fingerprinting, reconnaissance, and exploitation phases of an application server attack. | https://github.com/hatRiot/clusterd |
| cmospwd | 5.0 | Decrypts password stored in CMOS used to access BIOS setup. | http://www.cgsecurity.org/wiki/CmosPwd |
| cms-explorer | 1.0 | Designed to reveal the specific modules, plugins, components and themes that various cms driven websites are running | http://code.google.com/p/cms-explorer |
| cms-few | 0.1 | Joomla, Mambo, PHP-Nuke, and XOOPS CMS SQL injection vulnerability scanning tool written in Python. | http://packetstormsecurity.com/files/64722/cms_few.py.txt.html |
| codetective | 37.f94d9e8 | A tool to determine the crypto/encoding algorithm used according to traces of its representation. | https://www.digitalloft.org/init/plugin_wiki/page/codetective |
| complemento | 0.7.6 | A collection of tools for pentester: LetDown is a powerful tcp flooder ReverseRaider is a domain scanner that use wordlist scanning or reverse resolution scanning Httsquash is an http server scanner, banner grabber and data retriever | http://complemento.sourceforge.net |
| conscan | 1.1 | A blackbox vulnerability scanner for the Concre5 CMS. | http://nullsecurity.net/tools/scanner.html |
| cookie-cadger | 1.07 | An auditing tool for Wi-Fi or wired Ethernet connections. | https://cookiecadger.com/ |
| cowpatty | 4.6 | Wireless WPA/WPA2 PSK handshake cracking utility | http://www.wirelessdefence.org/Contents/Files/ |
| cpfinder | 0.1 | This is a simple script that looks for administrative web interfaces. | http://packetstormsecurity.com/files/118851/Control-Panel-Finder-Script.html |
| cppcheck | 1.66 | A tool for static C/C++ code analysis | http://cppcheck.wiki.sourceforge.net/ |
| cpptest | 1.1.2 | A portable and powerful, yet simple, unit testing framework for handling automated tests in C++. | http://cpptest.sourceforge.net/ |
| crackhor | 2.ae7d83f | A Password cracking utility. | https://github.com/CoalfireLabs/crackHOR |
| crackle | 39.3e93196 | Crack and decrypt BLE encryption | https://github.com/mikeryan/crackle/ |
| crackserver | 31.c268a80 | An XMLRPC server for password cracking. | https://github.com/averagesecurityguy/crack |
| create-ap | 103.9d78068 | This script creates a NATed or Bridged WiFi Access Point. | https://github.com/oblique/create_ap |
| creddump | 0.3 | A python tool to extract various credentials and secrets from Windows registry hives. | https://code.google.com/p/creddump/ |
| creds | 8181.da07974 | Harvest FTP/POP/IMAP/HTTP/IRC credentials along with interesting data from each of the protocols. | https://github.com/DanMcInerney/creds.py |
| creepy | 137.9f60449 | A geolocation information gatherer. Offers geolocation information gathering through social networking platforms. | http://github.com/ilektrojohn/creepy.git |
| crunch | 3.6 | A wordlist generator for all combinations/permutations of a given character set. | http://sourceforge.net/projects/crunch-wordlist/ |
| cryptcat | 1.2.1 | A lightweight version of netcat with integrated transport encryption capabilities. | http://sourceforge.net/projects/cryptcat |
| crypthook | 16.bceeb0b | TCP/UDP symmetric encryption tunnel wrapper. | https://github.com/chokepoint/CryptHook |
| cryptonark | 0.4.9 | SSL security checker. | http://blog.techstacks.com/cryptonark.html |
| csrftester | 1.0 | The OWASP CSRFTester Project attempts to give developers the ability to test their applications for CSRF flaws. | http://www.owasp.org/index.php/Category:OWASP_CSRFTester_Project |
| ctunnel | 0.6 | Tunnel and/or proxy TCP or UDP connections via a cryptographic tunnel. | http://nardcore.org/ctunnel |
| cuckoo | 1.1.1 | A malware analysis system. | http://cuckoosandbox.org/ |
| cupp | 3.0 | Common User Password Profiler | http://www.remote-exploit.org/?page_id=418 |
| cutycapt | 10 | A Qt and WebKit based command-line utility that captures WebKits rendering of a web page. | http://cutycapt.sourceforge.net/ |
| cvechecker | 3.5 | The goal of cvechecker is to report about possible vulnerabilities on your system, by scanning the installed software and matching the results with the CVE database. | http://cvechecker.sourceforge.net/ |
| cymothoa | 1 | A stealth backdooring tool, that inject backdoors shellcode into an existing process. | http://cymothoa.sourceforge.net/ |
| darkbing | 0.1 | A tool written in python that leverages bing for mining data on systems that may be susceptible to SQL injection. | http://packetstormsecurity.com/files/111510/darkBing-SQL-Scanner.1.html |
| darkd0rk3r | 1.0 | Python script that performs dork searching and searches for local file inclusion and SQL injection errors. | http://packetstormsecurity.com/files/117403/Dark-D0rk3r.0.html |
| darkjumper | 5.8 | This tool will try to find every website that host at the same server at your target | http://sourceforge.net/projects/darkjumper/ |
| darkmysqli | 1.6 | Multi-Purpose MySQL Injection Tool | https://github.com/BlackArch/darkmysqli |
| darkstat | 3.0.718 | Network statistics gatherer (packet sniffer) | http://dmr.ath.cx/net/darkstat/ |
| davoset | 1.2 | A tool for using Abuse of Functionality and XML External Entities vulnerabilities on some websites to at Go to link download Read more »
Saturday, April 1, 2017Tor 0 2 5 10 Anonymity Online Tor 0 2 3 x is deprecated!Tor 0 2 5 10 Anonymity Online Tor 0 2 3 x is deprecated! Tor 0.2.5.10 is the first stable release in the 0.2.5 series. It adds several new security features, including improved denial-of-service resistance for relays, new compiler hardening options, and a system-call sandbox for hardened installations on Linux (requires seccomp2). The controller protocol has several new features, resolving IPv6 addresses should work better than before, and relays should be a little more CPU-efficient. Weve added support for more OpenBSD and FreeBSD transparent proxy types. Weve improved the build system and testing infrastructure to allow unit testing of more parts of the Tor codebase. Finally, weve addressed several nagging pluggable transport usability issues, and included numerous other small bugfixes and features mentioned below. This release marks end-of-life for Tor 0.2.3.x; those Tor versions have accumulated many known flaws; everyone should upgrade. Below we list all changes in 0.2.5.10 since the 0.2.4.x series; for a list of changes in individual alpha releases, see the ChangeLog. Changes in version 0.2.5.10 - 2014-10-24
Subscribe to:
Posts (Atom)
|